In our continuing effort to deliver the best possible user experience, the Hybrid Analysis website will be undergoing scheduled maintenance on Tuesday, September 3. During this brief maintenance window – which is expected to last for 30 minutes, starting at 6AM PST – any detonations submitted will remain pending until the work by our team is complete. However, all other features of hybridanalysis.com will continue to be fully operational during the process.
We thank our community for your loyalty and look forward to continuing to be your preferred choice for free malware analysis. Once again, interruption to Hybrid Analysis users will be minimal and limited to the 30 minute delay in any detonations submitted during the scheduled maintenance window.
IT security blog focusing on malware forensics, dynamic and static analysis, as well as automated malware analysis techniques.
Wednesday, January 24, 2024
Hybrid Analysis Kicks Off 2024 With a Fresh Look and New Features

New Hybrid Analysis logo and fresh look as we kick-start 2024
Image scanning support and feedback contact form are now available
To celebrate the start of a new year, Hybrid Analysis — your favorite free public malware analysis platform — is kicking off 2024 with a fresh, modern new look and some additional new features and improvements intended to provide the best possible outcomes for our community.
For the past year we’ve been hard at work making under-the-hood performance optimizations. We’ve also added new features, such as support for file detonations in Windows 11 64-bit and x86 macOS, as well as a new “Analysis Related URLs'' category in the CrowdStrike AI section of the sample detonation report, which presents data on URLs and domains extracted from analyzed samples. We have also integrated new technologies from our partners including Bfore.Ai, ScamAdviser and CleanDNS.
New Logo, Refreshed Looks
Vintage is in, but there is such a thing as hanging on to a look for too long — and the Hybrid Analysis logo was beginning to look dated. We wanted a modern look that reflects the exciting new capabilities added to the service over the past year. In addition to the new logo, the Hybrid Analysis website has been refreshed with new fonts for added visual appeal.
These changes will become immediately apparent as you visit the homepage or navigate to any overview or report page. We’re constantly working to improve the Hybrid Analysis user experience, so through the upcoming year we plan to gently roll out new visual modifications and updates to enhance your experience with the platform.
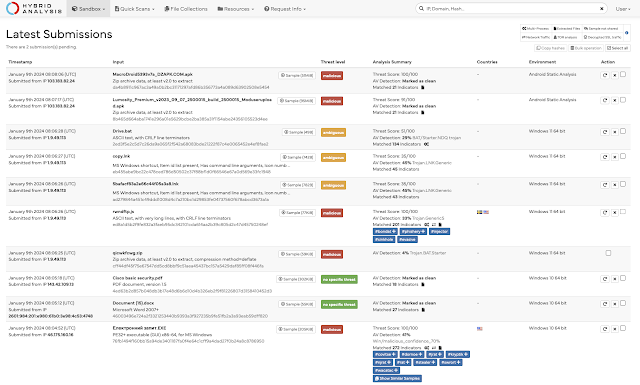
Figure 1. Hybrid Analysis Latest Submissions page with new font and logo
Image Scanning Support for QuickScan
Rest assured, the new changes are not just skin-deep. We just introduced new image-scanning support for QuickScan static analysis. It's as easy as uploading a 'png', 'jpg', 'gif', 'tiff', or 'bmp' file type and hitting the Analyze button. If you’re ever in doubt whether an image file type could be carrying some concealed executable code or malware, you can instantly get an assessment from QuickScan, which performs static analysis using CrowdStrike machine learning (ML) and technologies from our partners, such as Metadefender.
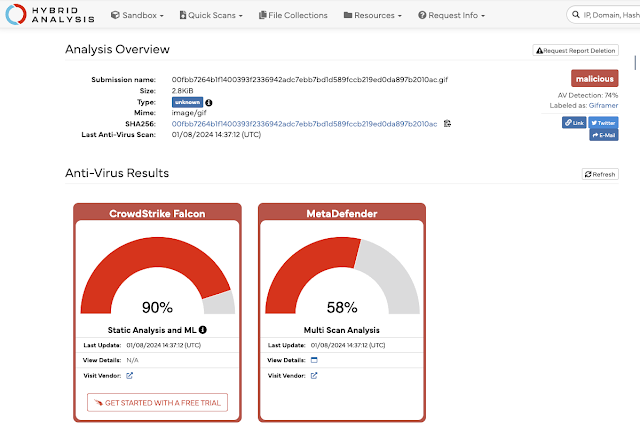
Figure 2. Hybrid Analysis QuickScan Analysis Overview for a ‘gif’ file
We Value Your Input
Hybrid Analysis vetted users now have the ability to conveniently ask questions, make suggestions or offer feedback about the platform. We have introduced a “Contact Us” form — found at the bottom of the webpage in the footer — so it’s easier than ever to reach out to us. Just pick one of the predefined topics from the Subject drop down list, blast us a message and we will do our best to reply to the email address associated with your Hybrid Analysis account.
Alternatively, for those that are not vetted users and want to reach out with comments, suggestions or feedback, please feel free to drop us a line on our Hybrid Analysis X (formerly Twitter) account. Your feedback is important to us and we value your input!
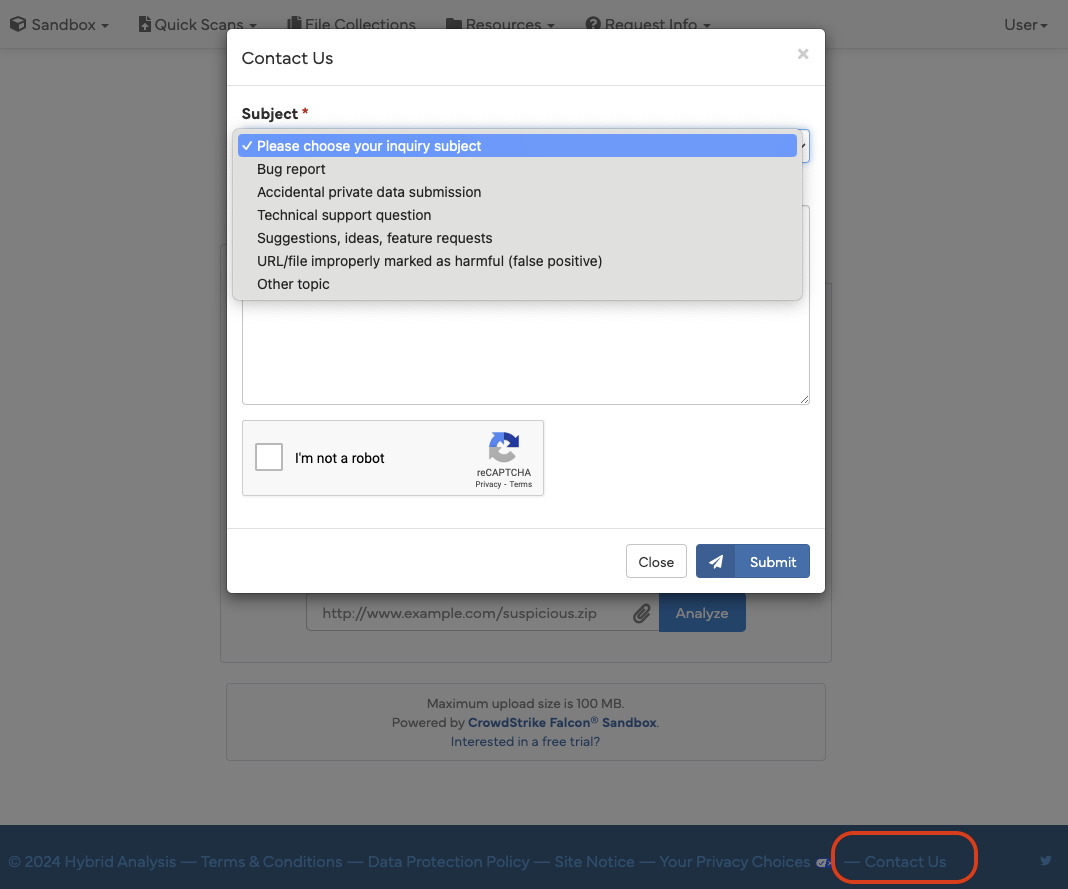
Figure 3 - Hybrid Analysis Contact Us form (available for vetted users)
The Road Ahead
We have been committed to continually improving the capabilities and the quality of the Hybrid Analysis platform by constantly adding new features, improving existing ones or in some cases, removing them.
Thank you to our users. You can look forward to continued investment in Hybrid Analysis upgrades through 2024. Expect ongoing improvements to the UI and, most importantly of all, continued enhancements to our services along with more technology partnerships to augment our capabilities for providing the best possible insights for you — the Hybrid Analysis community.

Tuesday, March 14, 2023
Hybrid Analysis Partners with ScamAdviser and CleanDNS to Provide Enhanced Context to URL and Domain Analysis
Hey everyone, we’ve got some exciting news to share! We are thrilled to announce our newest partnerships and technology integrations, with ScamAdviser and CleanDNS. These relationships will provide the Hybrid Analysis community with more context into analyzed URLs and domains. This augments our capabilities for providing the best possible insights for the Hybrid Analysis community.
We constantly strive to provide the most effective and comprehensive threat analysis platform to our community and these new integrations will enable the community to better understand threats and make more informed decisions on how to analyze or respond to them.
So, what exactly do these integrations offer our community?
Both ScamAdviser and CleanDNS will be presented as Scorecards in the Analysis Overview section. Clicking the View Details button will open a modal with additional context and information on the analyzed domain. Apart from Domain Scam Score and Domain Abuse Reports, users also have the option of visiting each partners’s website for further details on the analyzed domain.

Fig. 1 Scorecards in the Analysis Overview section displaying the ScamAdviser and CleanDNS integration

Fig. 2 Modal view for the CleanDNS View Details button
ScamAdviser utilizes over 40 data sources such as the IP address of the web server, the availability of contact details on the website, the age of the URL and ratings on review sites. The service is designed to assist in making informed decisions regarding the scam-like behavior of URLs. Its algorithm determines whether a website is legitimate – with genuine reviews – or a phishing site selling fake products. By integrating ScamAdvisor into the Hybrid Analysis platform with its 30 million analyzed websites, we will be able to provide researchers and analysts with a more comprehensive understanding of the URLs we analyze. For more information on how the technology behind it works, feel free to check out the ScamAdviser website.
CleanDNS offers a vital solution for detecting likely sources of abuse. It is a valuable tool for assisting registries, registrars and researchers in making informed decisions to take action against such abuse. Initially informed by reputable abuse data sources including top domain abuse feeds, commercial, non-profit and academic DNS abuse feeds, CleanDNS enhances abuse records with an evidence-based workflow to create actionable reports. With CleanDNS, we can provide our community with an additional layer of context regarding the state of analyzed domains. For more information on how the technology behind it works, feel free to check out the CleanDNS website.
These partnerships with ScamAdviser and CleanDNS enable Hybrid Analysis researchers and analysts to identify fraud, phishing scams, and other malicious activities. By leveraging these capabilities, we are augmenting our already powerful platform, providing the community with additional insights into the behavior of a URL or domain. We look forward to continuing to collaborate and partner with technology providers to offer additional tools and improve threat research insights for our security community.
Happy Hunting!
Tuesday, June 8, 2021
Public Service Announcement: Retiring Falcon Sandbox Public API V1 Starting August 3, 2021
We are announcing the sunset of Falcon Sandbox Public API v1, which will reach end of life as of August 3, 2021, 12:00 PM EST. After this date, the Falcon Sandbox Public API v1 will stop responding altogether.
Here at Hybrid Analysis, we are dedicated to enabling our community to leverage a unified platform for automated malware forensics by concentrating our efforts on improving our systems to deliver the best experience, performance, features, and tools to enrich malware analysis.
Anyone visiting the Hybrid Analysis homepage has probably already seen the banner about retiring the Falcon Sandbox Public API v1, and we have already started notifying API connectors authors about version removal.


Falcon Sandbox Public API v2 has been in use for more than a year, and we’ve made great efforts to integrate existing API v1 features into API v2, while also expanding on them.
Who is Impacted?
This change impacts everyone that has been using the Falcon Sandbox Public API v1. Starting today June 8, 2021, the Falcon Sandbox Public API v1 has entered the sunset period, leading to deprecation beginning August 3, 2021,12:00 PM EST.
Anyone using the VxWebService Python API Connector v2 with the Falcon Sandbox Public API v2 will not be impacted and the code that resides in the master branch of that repository supports API v2.
As a reminder, the legacy VxWebService app utilising API v1 is not supported anymore, but still available in the v1 branch.
Why the Change to Falcon Sandbox Public API v2?
As some of you have already noticed when using the API v2, one of the major benefits involves using OpenAPI and Swagger Docs, which have become the world standard for defining RESTful interfaces.
Data security and privacy are also something we take seriously, so the fact that Falcon Sandbox Public API v2 is also SOC II compliant is all the more critical. This means the API v2 is built around the five “trust service principles” involving security, availability, processing integrity, confidentiality and privacy.
But most importantly, with Falcon Sandbox Public API v2 we can readily and constantly roll out new features that can help you, the research community, expand on analysis capabilities while offering a reliable API standard that’s easy to use.
For a complete list of features and functionalities we have added over time into the Falcon Sandbox Public API v2, check out our API v2 changelog section (here)
How to Successfully Migrate to Falcon Sandbox Public API v2?
Throughout the sunsetting phase, those who still use the API v1 are encouraged to switch to the API v2 by following the instructions we have put together (here).
If you have any automation dependencies running on Falcon Sandbox Public API v1, please make the necessary changes and switch to Falcon Sandbox Public API v2 using the available documentation.
We hope this graceful transition will not bring too much disruption to your activities. If you experience any issues with the migration process or if you have suggestions on new features that you would like to have available, please let us know.
Happy Hunting!
Wednesday, April 7, 2021
Upcoming Maintenance - April 7th, 2021 2AM EST - 3AM EST
Hello again HA Community! The CrowdStrike Falcon Sandbox team hopes you are doing well, and staying safe during these unprecedented times. As always, thank you for being a part of the biggest community-focused sandbox service! Our goal is to continually enhance your experience by not only delivering new and useful features to assist in malware analysis, but also by maintaining a stable and efficient platform.
As such, we have scheduled a brief downtime window from 2AM - 3AM EST on April 7th, 2021 to perform critical maintenance. During this downtime the site will be unavailable. We appreciate your patience during this brief interruption and look forward to seeing you back!
Happy Hunting!
Thursday, December 3, 2020
Network Simulation now live on Hybrid-Analysis!
We are proud to announce the availability of Network Simulation for file and URL detonations on Hybrid-Analysis.com!
Network Simulation will block internet-bound traffic from reaching its destination, instead routing all traffic to an internal endpoint which responds to those outbound requests (DNS/HTTP(s)/etc...). This allows the submitter to collect crucial indicators and detonation details without ever directly contacting attacker-controlled infrastructure.
To utilize this new feature, submit a new file or URL for analysis and expand "Runtime Options" found within the environment selector section:

Then select "Simulate Network Traffic" when customizing your detonation parameters:

That's it! When your sample is submitted, all traffic destined for the internet will be safely routed internally to feign internet availability.
Happy Hunting!
Wednesday, August 12, 2020
New and Improved Threat Score!
Greetings from Sandboxland! From all of us at Hybrid Analysis, we hope this message finds you healthy and well. It’s been quite a long time since our last blog post… we’ve been busy working on platform enhancements and introducing new features to further improve your sandbox experience. One of the most exciting new features is the integration of a machine-learning powered threat score!
With this new feature, the sample and pertinent sandbox data will be scrutinized by a machine-learning model developed with CrowdStrike’s proven machine-learning technology, returning a threat score and associated verdict. The objective of this undertaking was to achieve greater sensitivity and specificity while computing threat scores. Initial analysis from a data set consisting of ~40K samples shows the new methodology to be quite effective, with a significant decrease in the False Positive Rate (FPR), while simultaneously increasing the True Positive Rate (TPR). This feature is initially limited to non-URL submissions detonated in our Windows detonation environments with plans for further expansion as the model develops and matures.
Subscribe to:
Posts (Atom)